You click on a site, a banner pops up asking you to “accept cookies,” and you click accept without reading it, the same as everyone else. Most people have never actually gotten a straight answer on what that button does or what they just agreed to.
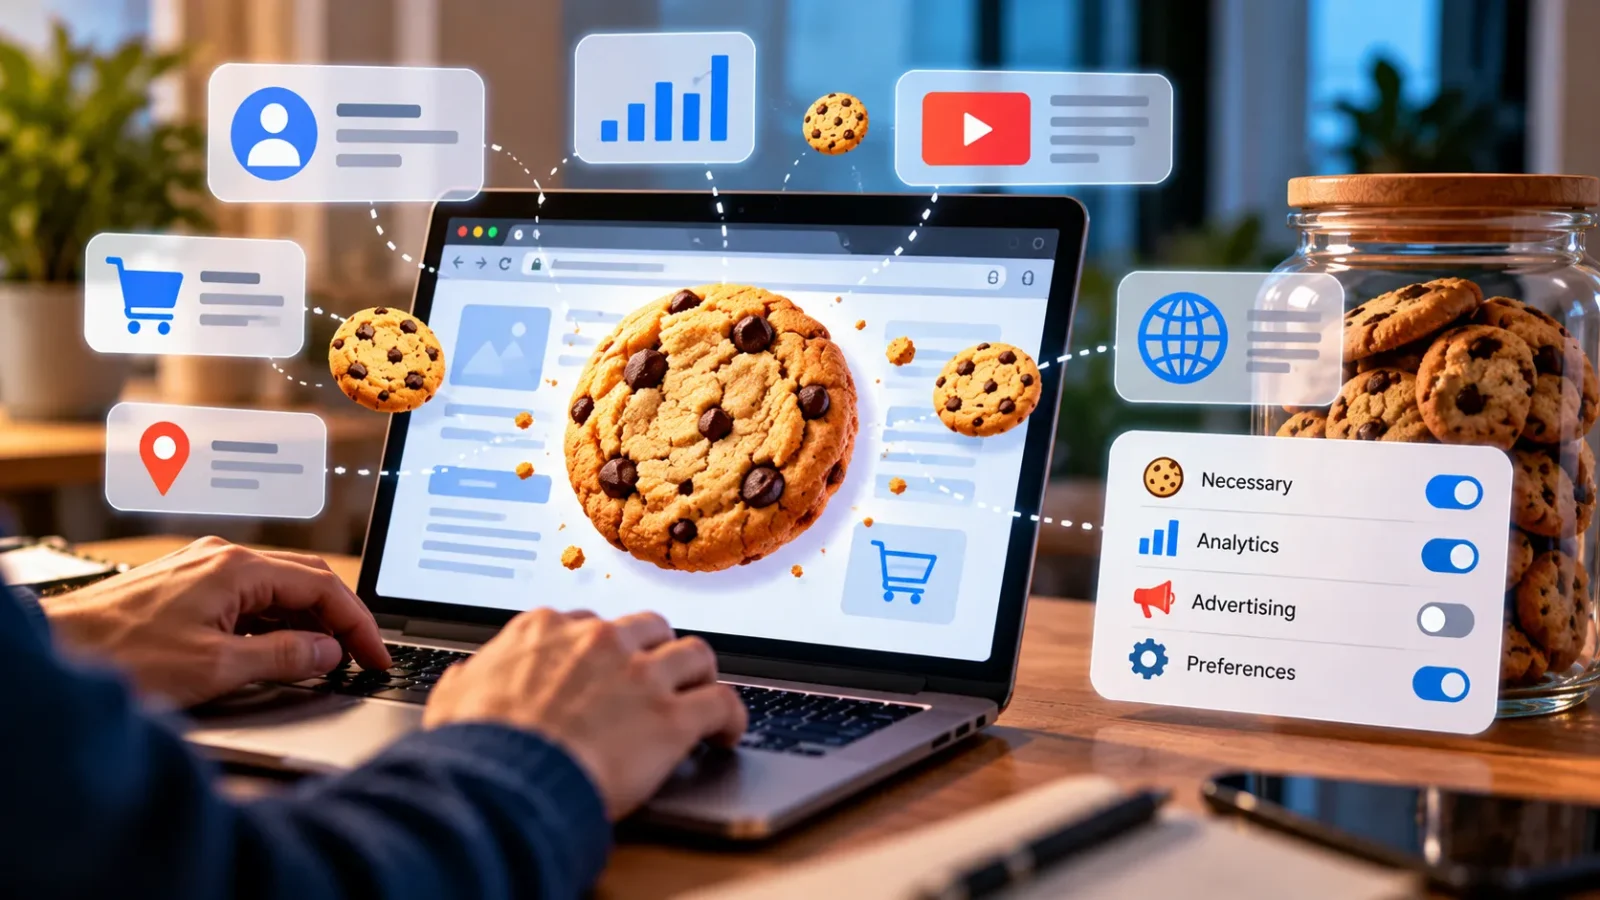
Cookies are small text files a website saves on your device to remember information about you, like whether you’re logged in, what’s in your cart, or what language you prefer. They’re not programs; they can’t run code on their own, and in most cases they’re not dangerous. But some cookies do track your activity across other websites, and that’s the part worth understanding before you tap “accept” again.
Below is exactly what cookies are, what they’re used for, how they track you, and honest answers to whether you should accept or reject them.
What Are Cookies on a Website?
A cookie is a small piece of text, usually just a few kilobytes, that a website sends to your browser, which then saves it on your device. The next time you visit that site, your browser sends the cookie back, and the site uses it to recognize you.
Cookies are a memory system for websites, since the web itself has no built-in way to remember who you are between page loads. Cookies fill that gap. Without them, every page you loaded would treat you as a brand-new visitor. You’d get logged out every time you clicked a link.
What Are Cookies Used For?
Three main jobs, and almost every cookie you’ll ever encounter falls into one of these:
- Keeping you logged in. A session cookie proves to the site that you already signed in, so you don’t have to re-enter your password on every page.
- Remembering your preferences. Language, currency, dark mode, items left in a shopping cart. Cookies hold onto this between visits.
- Tracking behavior. Some cookies record what you click, how long you stay, and what pages you visit, either on that one site (analytics) or across many sites (advertising).
That third use is where most of the privacy concern actually comes from, and it’s worth its own section below.
What Does It Mean When a Website Uses Cookies?
It means the site is storing small files on your device to remember something about your visit, nothing more dramatic than that. Under laws like GDPR in the EU and similar rules elsewhere, sites are required to tell you this and ask permission before setting most cookies, which is exactly why you see that consent banner.
How Do Cookies Track You?
A third-party cookie gets set not by the site you’re visiting, but by an ad network or analytics company whose code is embedded on that page. If the same ad network’s code sits on hundreds of different websites, it can read its own cookie on each one, meaning it sees that the same browser visited a news site, then a shoe store, then a travel site, and builds a behavioral profile from that pattern.
A tracking pixel works alongside this: a tiny, invisible image loaded from the ad network’s server, which triggers a cookie check every time it loads, even if you never click anything. This combination is how you can look at running shoes on one site and then see ads for the same shoes following you around completely unrelated websites days later.
First-party cookies, set directly by the site you’re actually on, don’t do this. Other websites can’t read them, so they’re the much less concerning category of the two.
What Are Cookies In Cyber Security?
A cookie is treated as a potential attack target, not just a convenience feature, and this is a gap most cookie explainers skip entirely.
The real risks:
- Session hijacking. If an attacker steals your session cookie through an unsecured Wi-Fi network or a malicious script, they can impersonate your logged-in session without ever knowing your password.
- Cross-site scripting (XSS). A vulnerable website can be tricked into running malicious code that reads and steals cookies from anyone who visits.
- Cross-site request forgery (CSRF). An attacker uses your existing logged-in cookie against you, tricking your browser into acting on a site you’re authenticated on, without your knowledge.
Two settings largely prevent these: the Secure flag (a cookie only sent over encrypted HTTPS connections) and the HttpOnly flag (a cookie that JavaScript on the page can’t read directly, which blocks most XSS-based cookie theft). Reputable sites set both by default. You don’t need to configure this as a visitor, but it’s worth knowing that not every site does it correctly.
What Are Cookies? Are They Safe?
Mostly, yes. A cookie is just text. It cannot carry a virus, install software, or run code on your device by itself. That’s the honest, direct answer to “are they safe,” and it holds true for the overwhelming majority of cookies you’ll ever encounter.
The actual risk isn’t the cookie itself. It’s what happens if one gets stolen (see the security risks above) or how much tracking data gets built up from third-party cookies over time. Neither of those makes cookies inherently unsafe technology; they’re reasons to be selective about which cookies you accept, not reasons to panic about the concept.
Types of Cookies
| Type | What it does |
|---|---|
| Session cookie | Deleted when you close your browser |
| Persistent cookie | Stays for a set period, sometimes up to two years |
| First-party cookie | Set by the site you’re on; can’t be read elsewhere |
| Third-party cookie | Set by an embedded ad or analytics network; used for cross-site tracking |
| Essential cookie | Required for basic site function, like staying logged in |
| Zombie/supercookie | Recreates itself after deletion, the most invasive category, and increasingly blocked by modern browsers |
What Are Cookies in Chrome, And How Do I Manage Them?
Chrome stores cookies per site and gives you full control over them. To check or manage:
- Open Chrome and click the three dots in the top right, then Settings.
- Go to Privacy and security > Cookies and other site data.
- Choose to block third-party cookies, block all cookies, or clear existing ones.
- To check or delete cookies for one specific site, click the icon to the left of the address bar while on that site, then Cookies and site data.
Chrome has been phasing out third-party cookie support by default for standard browsing, which is part of a broader industry shift away from cross-site tracking. Safari and Firefox block third-party cookies by default already.
What Does Accept Cookies Mean?
Accept cookies means that you’re agreeing to let that site (and any third parties embedded on it, like ad networks) set and read cookies on your device for the purposes listed in the consent banner, usually a mix of essential function, analytics, and advertising. Rejecting cookies where the site allows it typically still lets essential cookies through (the site usually can’t function without them) but blocks the optional tracking and advertising ones.
Frequently Asked Questions
Are cookies bad for your computer?
No. Cookies are plain text files, not programs. They can’t install malware, run code, or damage your device. The concern with cookies is privacy and tracking, not computer safety.
Should I accept cookies?
For sites you trust and use regularly, accepting is usually fine and makes the site work better. For sites you’re visiting once, or on banners that bundle in a lot of third-party advertising trackers, rejecting the optional ones (most consent banners let you customize this) is the more privacy-conscious choice.
What happens if you reject cookies?
Essential cookies usually still load so the site functions. Still, you’ll typically get logged out between visits, lose saved preferences, and may see less personalized (but not necessarily fewer) ads, since some sites fall back to less targeted advertising methods instead.
Do I delete cookies?
You can, and doing it occasionally is a reasonable habit. It clears out old tracking data and can fix some login or site-loading glitches. It also logs you out of sites and clears saved preferences, so you’ll need to sign back in afterward. Neither doing it nor skipping it is required for basic safety.
The Bottom Line
Cookies are small text files, not a threat by default. First-party ones mostly just make websites work better, and third-party ones are what actually track you across the web. Accept them on sites you trust, be more selective on ones you don’t, and know neither choice puts your computer at risk.